Jmix version: 1.1.2
Jmix Studio plugin version: 1.1.4-213
IntelliJ IDEA 2021.3 CE - Build #IC-213.5744.223, built on November 27, 2021
Operating System: macOS 12.0.1 (21A559)
File System: Case-Sensitive Journaled HFS+ (APFS)
Datebase: PostgreSQL 13
Hi Everyone
How can I verify and use the Anonymous User functionality? I have read the documentation Users :: Jmix Documentation and experiemented with this code in the DatabaseUserRepository class with the provided FullAccessRole and also with my CUBA-to-Jmix migrated AnonymousUserRole …
but I do not understand how I can access my application at http://localhost:8080 without provoking the login-screen? I need to present the anonymous user with my other information screens before logging into the application, just like I do in CUBA.
I am hoping that the solution to number 1 will enable me to refactor my code for number 2. Note, that I also opened a completely new project to experiment with this but the result was the same as with my migrated project.
Thank you for the information and your efforts. I was able to activate the anonymous user access with these new appilcation properties and it is working with the AnonymousUserRole that I migrated from CUBA.
But I did find a behavior that is new and maybe a bug…
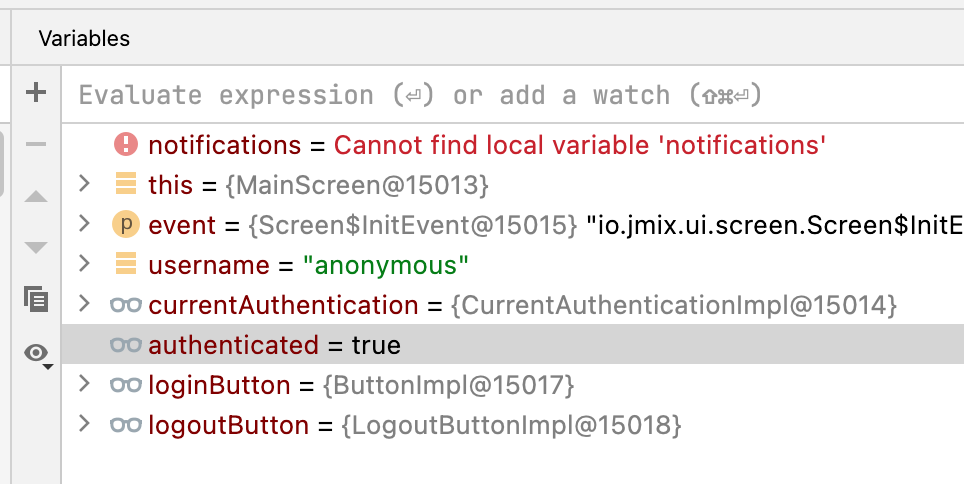
In CUBA the following code in my MainScreen onInit() controller-handler returned “false” for an anonymous user when visiting the application URL before a login screen is presented:
I can check the username in combination with this isAuthenticated() attribute to determine if the authenticated user is the “anonymous” user but I believe that this should not be necessary.
Can you please check this situation and give me further feedback. Thanks in advance.
That’s how Spring security works. The documentation says:
Note that there is no real conceptual difference between a user who is “anonymously authenticated” and an unauthenticated user. Spring Security’s anonymous authentication just gives you a more convenient way to configure your access-control attributes.
If you want to check that your authentication is anonymous you may do the following:
and authenticated is false for the “anonymous” user, which is the behavior that I was originally searching for. I have not thought about all of the different use cases, so I cannot recommend one solution over the other.
I was also able to refactor my MainScreen to re-implement most of the functionality described in point 2 above. If I have any more problems with that, I will open a new topic.