Hi Jmix Team,
Our security team inform us that our code has a critical vulnerability, our aplication is using the latest version 3.0.2. The recommended solution is to upgraded the embbebed TOMCAT from 11.0.24 to 11.0.25. We understand that this version come along with the Springboot version, ¿Is there any plan to upgrade the springboot version to a higher version with an upgraded Tomcat?
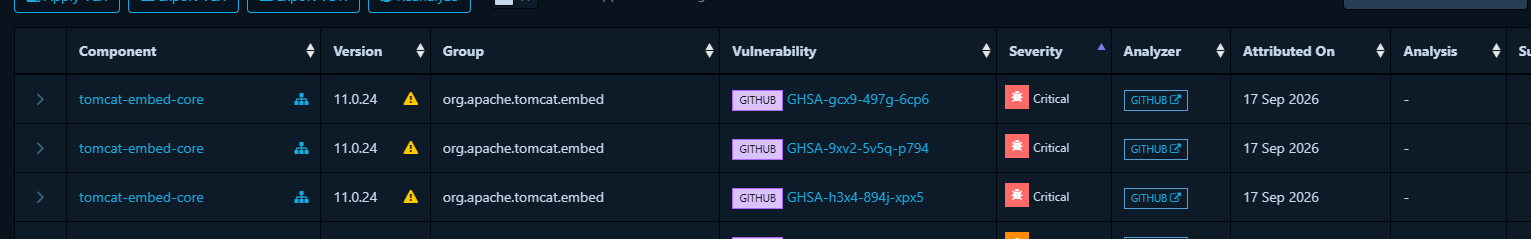
CVE-2026-65182 (NVD)
National Vulnerability Database
Improper Access Control, Incorrect Authorization vulnerability in Apache Tomcat leads to security constraint bypass if a constraint for a longer path is specified before a more restrictive constraint for a shorter sub-path.
This issue affects Apache Tomcat: from 11.0.0-M1 through 11.0.24, from 10.1.0-M1 through 10.1.57, from 9.0.0.M1 through 9.0.120, from 8.5.0 through 8.5.100, from 7.0.0 through 7.0.109.
Users are recommended to upgrade to version 11.0.25, 10.1.58, 9.0.121, which fixes the issue.