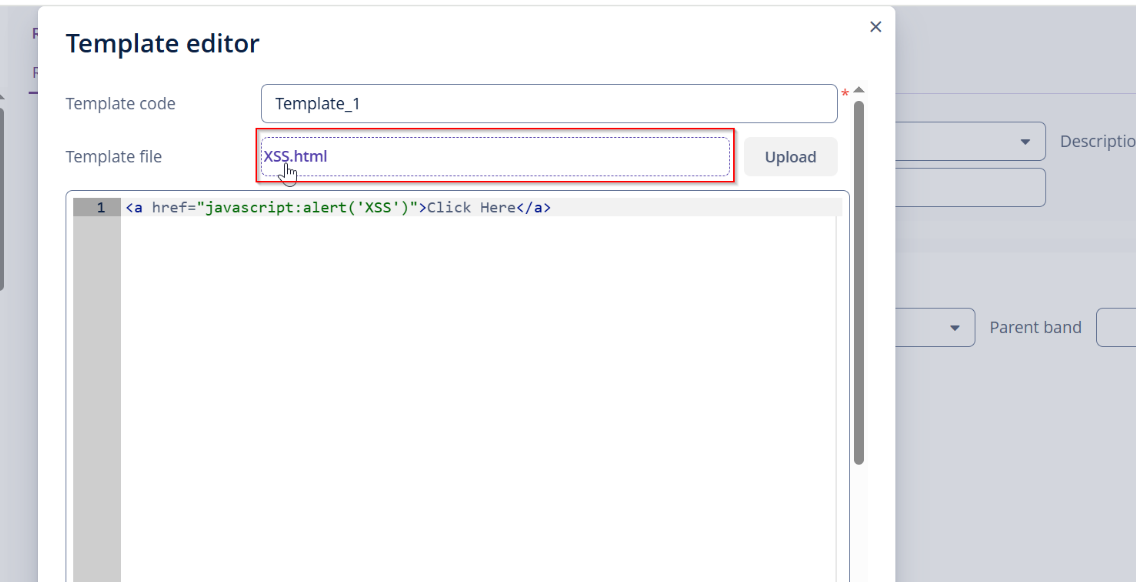
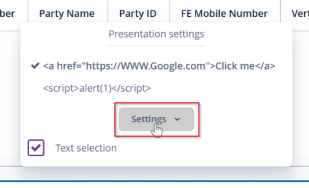
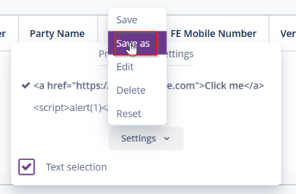
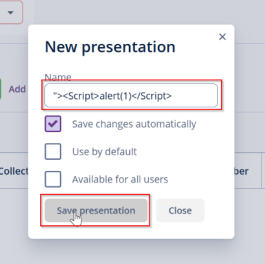
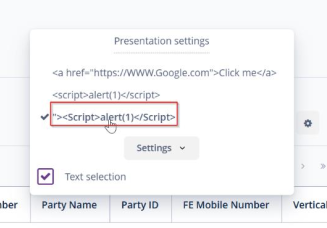
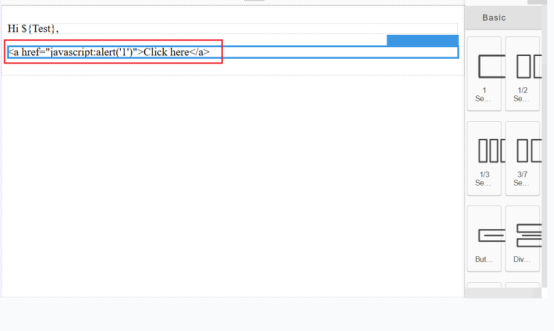
This vulnerability occurs when a web application allows users to upload files without proper
validation or sanitization, leading to the execution of malicious scripts. In this scenario, you
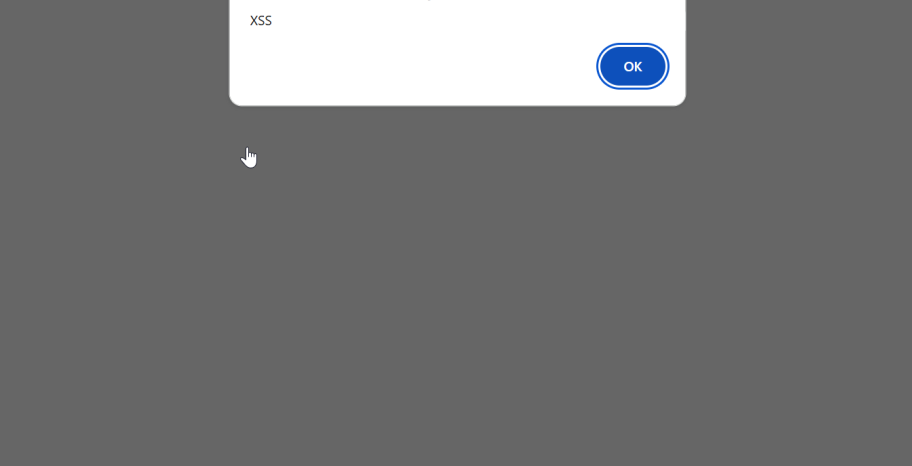
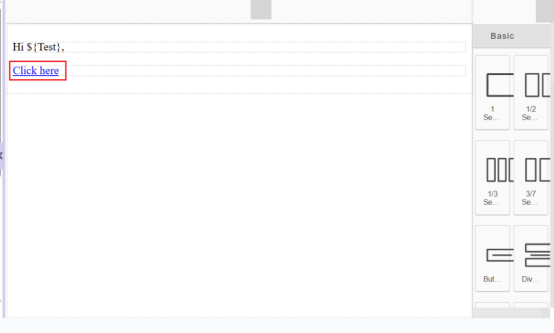
uploaded a file containing an XSS payload, and when clicking on the file name, the JavaScript
executed successfully, confirming the vulnerability. If exploited, an attacker can execute
arbitrary scripts in the context of a victim’s session, potentially leading to session hijacking,
phishing, or further attacks.
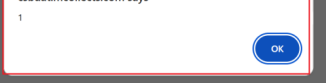
The XSS alert popup message was successfully displayed.
Is it possible to override below screen validate method to check whether the text enter to save does not contain javascript alert. @org.springframework.stereotype.Component(“ui_PresentationEditor”) @Scope(BeanDefinition.SCOPE_PROTOTYPE)
protected boolean validate() {
        TablePresentations presentations = component.getPresentations();

        //check that name is empty
        if (StringUtils.isEmpty(nameField.getValue()) && AppUI.getCurrent() != null) {
            AppUI.getCurrent().getNotifications()
                    .create(Notifications.NotificationType.HUMANIZED)
                    .withCaption(messages.getMessage("PresentationsEditor.error"))
                    .withDescription(messages.getMessage("PresentationsEditor.error.nameRequired"))
                    .show();
            return false;
        }

        //check that name is unique
        final TablePresentation pres = presentations.getPresentationByName(nameField.getValue());
        if (pres != null && !pres.equals(presentation) && AppUI.getCurrent() != null) {
            AppUI.getCurrent().getNotifications()
                    .create(Notifications.NotificationType.HUMANIZED)
                    .withCaption(messages.getMessage("PresentationsEditor.error"))
                    .withDescription(messages.getMessage("PresentationsEditor.error.nameAlreadyExists"))
                    .show();
            return false;
        }
        return true;
    }
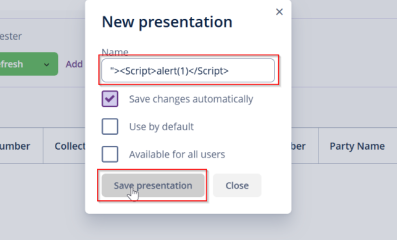
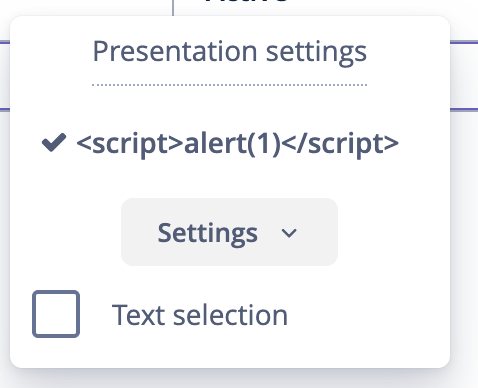
Could you please describe in more detail what the problem is with the presentation’s name field? As far as I see, the value is shown as is and isn’t used in the html output, i.e. isn’t executed.
I want to validate input properly , since it is able to craft the input in
a form that is not expected by the rest of the application. This can lead to parts of the system
receiving unintended input, which may result in altered control flow, arbitrary control of a
resource, or arbitrary code execution.
Also i similarly if i add this same script into email template without proper validation or sanitization, leading to the execution of injected malicious HTML or JavaScript.
I am just trying to restrict the script to avoid HTML Injection
Your screenshots prove that setting the HTML code as the presentation name has no effect (it’s not executed), except for the fact that the user can see that it is an HTML code. If you want to override PresentationEditor you can do it, since it’s a bean.